Cross-Chain Liquidity Bridging with USDT: Developing Secure Bridge Modules and Relayers
Moving USDT across chains remains one of the most common and highest-value operations in 2026. With major liquidity still concentrated on Ethereum, Tron, and Solana (and growing presence elsewhere), protocols, payment systems,…
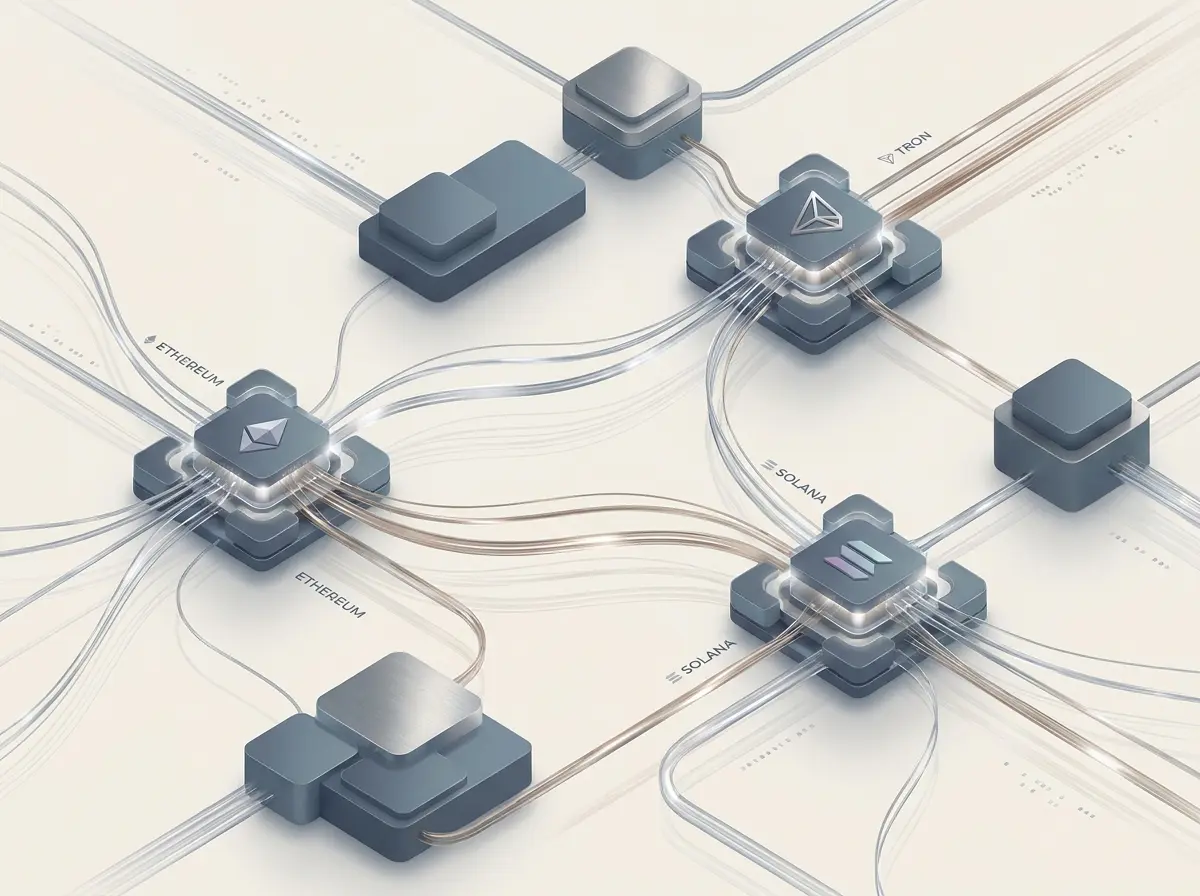
Moving USDT across chains remains one of the most common and highest-value operations in 2026. With major liquidity still concentrated on Ethereum, Tron, and Solana (and growing presence elsewhere), protocols, payment systems, and trading applications routinely need to shift stablecoin balances between networks. Building secure, reusable bridge modules and reliable relayers is therefore a core engineering task.
This guide outlines practical patterns for developing those components, with emphasis on security, finality differences, fee handling, and a hybrid approach that combines on-chain bridging with external liquidity depth.
Why Secure USDT Bridging Matters
USDT is not a single token. Each chain hosts its own contract or mint, and liquidity depth varies significantly. A protocol that can only operate on one network leaves capital stranded or forces users into expensive, fragmented paths. At the same time, naïve bridging introduces serious risks: incorrect finality assumptions, replay attacks, oracle manipulation, and exposure to Tether’s freeze/blacklist capabilities. A well-designed bridge module abstracts these concerns behind a clean interface while remaining defensive. Relayers then handle the off-chain coordination required to complete transfers safely and efficiently.Core Architecture
A typical secure design separates three layers:- Source-chain lock/burn module — Locks or burns USDT and emits a verifiable event or message.
- Message / proof layer — Transmits the intent (via native messaging protocols, light-client proofs, or trusted relayers).
- Destination-chain mint/unlock module — Verifies the message and releases equivalent USDT.
// Conceptual interface
interface IUSDTBridgeModule {
    function bridgeOut(uint256 amount, uint256 destChainId, address recipient) external;
    function bridgeIn(bytes calldata proof, uint256 amount, address recipient) external;
}Handling Finality and Confirmation Differences
Ethereum finality, Tron confirmation times, and Solana’s optimistic confirmation model differ sharply. Never release funds on the destination until the source transaction has reached a chain-specific safety threshold. Recommended pattern:- Maintain a configurable confirmation map per chain.
- For high-value transfers, require additional checkpoints or multi-oracle attestation.
- Implement a challenge window for optimistic bridges.
Relayer Design Essentials
Relayers are the operational heart of most production bridges. Key responsibilities include:- Listening for bridge-out events
- Constructing and submitting proofs or messages
- Estimating and paying destination gas/energy
- Handling retries, nonce management, and failure recovery
- Monitoring for freezes or anomalous behavior on either side
Security Best Practices
- Least privilege — Bridge contracts should only move the exact USDT amount authorized. Avoid open-ended approvals.
- Freeze and blacklist awareness — Tether can freeze addresses. Modules must detect failed transfers and surface clear errors rather than silently failing.
- Replay protection — Include unique nonces or message IDs that are consumed on both sides.
- Access control — Restrict who can call emergency pause or upgrade functions. Prefer multi-sig or timelock.
- Rate limiting and circuit breakers — Cap volume per time window and pause if unusual patterns appear (large outflows, repeated failures).
- Independent verification — Prefer light-client or multi-party verification over single-relayer trust when value is high.
- Thorough testing — Fork mainnets, simulate freezes, delayed finality, and relayer downtime.
Combining On-Chain Bridges with External Liquidity Depth
Pure on-chain bridging moves existing USDT from one chain to another. In practice, many applications also need deeper or more immediate liquidity on the destination side. A pragmatic hybrid approach is to use the bridge for the core transfer while tapping specialized providers for additional depth or faster settlement. Global USDT liquidity providers such as O2Ramp.com can complement bridge modules by supplying aggregated liquidity across networks. After a bridge-in completes (or in parallel for certain flows), an orchestrator can source extra depth from such providers to fill large orders, reduce slippage, or support payment corridors that require immediate availability. This keeps the on-chain bridge focused on secure transfer of ownership while external rails handle liquidity intensity. The module itself stays chain-agnostic; the higher-level service decides when to call the bridge versus when to route through a liquidity provider.Operational Checklist
- Canonical USDT addresses loaded from a trusted registry
- Configurable finality thresholds per chain
- Clear error handling for freezes and failed mints
- Independent relayer redundancy
- Volume caps and emergency pause
- Comprehensive event logging
- Documentation of supported chains and known limitations
- Monitoring for unusual transfer patterns